Details
-
Bug
-
Resolution: Fixed
-
 Major
-
None
-
Professional Edition
-
None
Description
Hello,
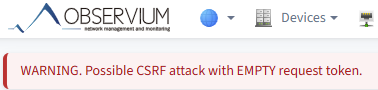
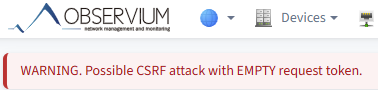
I had this warning and can't delete an existing syslog rule on my actual version 26.10.15358 (rolling)
"WARNING. Possible CSRF attack with EMPTY request token."
Could you check plz ?
Regards,